 |


|
#1
 12-04-2025, 01:30 PM |
||||
|
||||
 New Android malware sneak-wipes your bank account: Here’s how to avoid gett 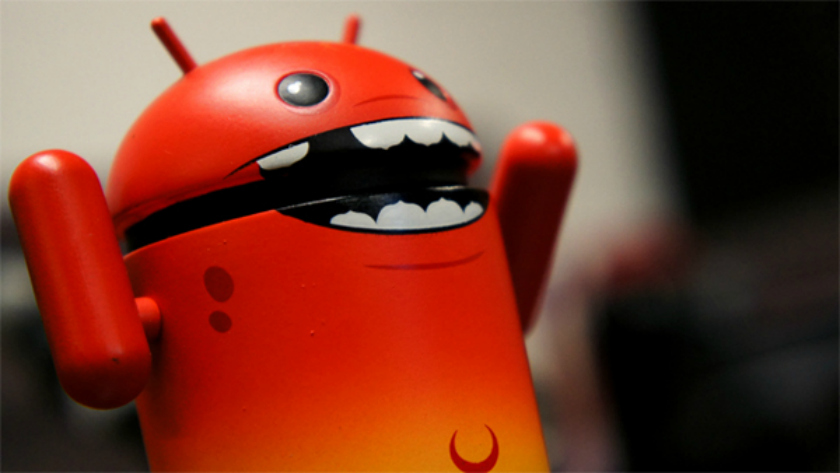 TL;DR
Researchers at Cleafy, an online fraud prevention firm, have discovered (via MalwareBytes) a new Android trojanware dubbed “Albiriox.” Just like Sturnus, which we learned about last week, Albiriox is distributed through infected or dummy APKs by luring potential targets into believing they are downloading actual apps. One of the ways that hackers use to achieve that is by creating fake replicas of Google Play Store listings, making users believe they are downloading apps from secure sources when they are actually not. Hackers also lure targets by posting fake promotions and offers, seeking contact details, and then delivering malicious APKs through messaging apps, such as WhatsApp and Telegram. More... 
|



  |
«
Previous Thread
|
Next Thread
»
| Currently Active Users Viewing This Thread: 1 (0 members and 1 guests) | |
|
|

All times are GMT -4. The time now is 12:17 AM.